Thủ Phủ Hacker Mũ Trắng Buôn Ma Thuột

Chương trình Đào tạo Hacker Mũ Trắng Việt Nam tại Thành phố Buôn Ma Thuột kết hợp du lịch. Khi đi là newbie - Khi về là HACKER MŨ TRẮNG !

Hacking Và Penetration Test Với Metasploit

Chương trình huấn luyện sử dụng Metasploit Framework để Tấn Công Thử Nghiệm hay Hacking của Security365.

Tài Liệu Computer Forensic Của C50

Tài liệu học tập về Truy Tìm Chứng Cứ Số (CHFI) do Security365 biên soạn phục vụ cho công tác đào tạo tại C50.

Sinh Viên Với Hacking Và Bảo Mật Thông Tin

Cuộc thi sinh viên cới Hacking. Với các thử thách tấn công trang web dành cho sinh viên trên nền Hackademic Challenge.

Tấn Công Và Phòng Thủ Với BackTrack / Kali Linux

Khóa học tấn công và phòng thủ với bộ công cụ chuyên nghiệp của các Hacker là BackTrack và Kali LINUX dựa trên nội dung Offensive Security

Sayfalar

Showing posts with label DLL Injector. Show all posts

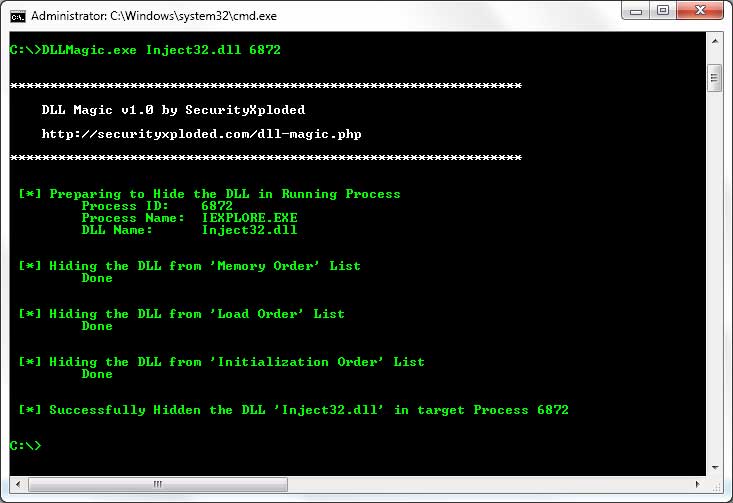
[DLL Magic] Tool to Hide DLL in any Windows Process


DLL Magic is the simple command-line tool to Hide DLL in any Windows Process.


Every Process maintains internal database of loaded Modules/DLLs in the form of three linked lists. Each of these linked list represents the order in which DLLs are loaded, here are they

  • Load Order
  • Memory Order
  • Initialization Order

DLL Magic hides the DLL by removing the DLL from all these three linked lists.

This is an effective technique to hide DLL from any of the Process/DLL listing tools. And it is the common method used by Rootkits to hide their presence. However such hidden DLLs are visible in Kernel based tools.

Though 'DLL Magic' works on both 32-bit & 64-bit systems, it can Hide DLL from 32-bit Process only.

It is primarily useful for developers and researchers. Also being command-line tool makes it easy to use in automation scripts.
It works all platforms starting from Windows XP to Windows 8.

[RemoteDLLInjector] Command-line Tool to Inject DLL into Remote Process


Remote DLL Injector is the free command-line tool to Inject DLL into remote process.

Currently it supports DLL injection using the CreateRemoteThread technique. If you are looking for advanced and more user friendly GUI version then check out our popular RemoteDll tool.

Being a command-line tool makes it easy to integrate into your automation scripts. Also useful when you are remotely operating on the system especially during Pen Testing situations.

One of the unique feature of Remote DLL Injector is its ability Inject DLL into ASLR enabled processes. It dynamically calculates DLL and function offsets within target process before the injection operation.

It is fully portable and includes both 32-bit & 64-bit versions. It has been successfully tested on all platforms starting from Windows XP to Windows 8.


Download RemoteDLLInjector

More information: securityxploded.com/remote-dll-injector.php